
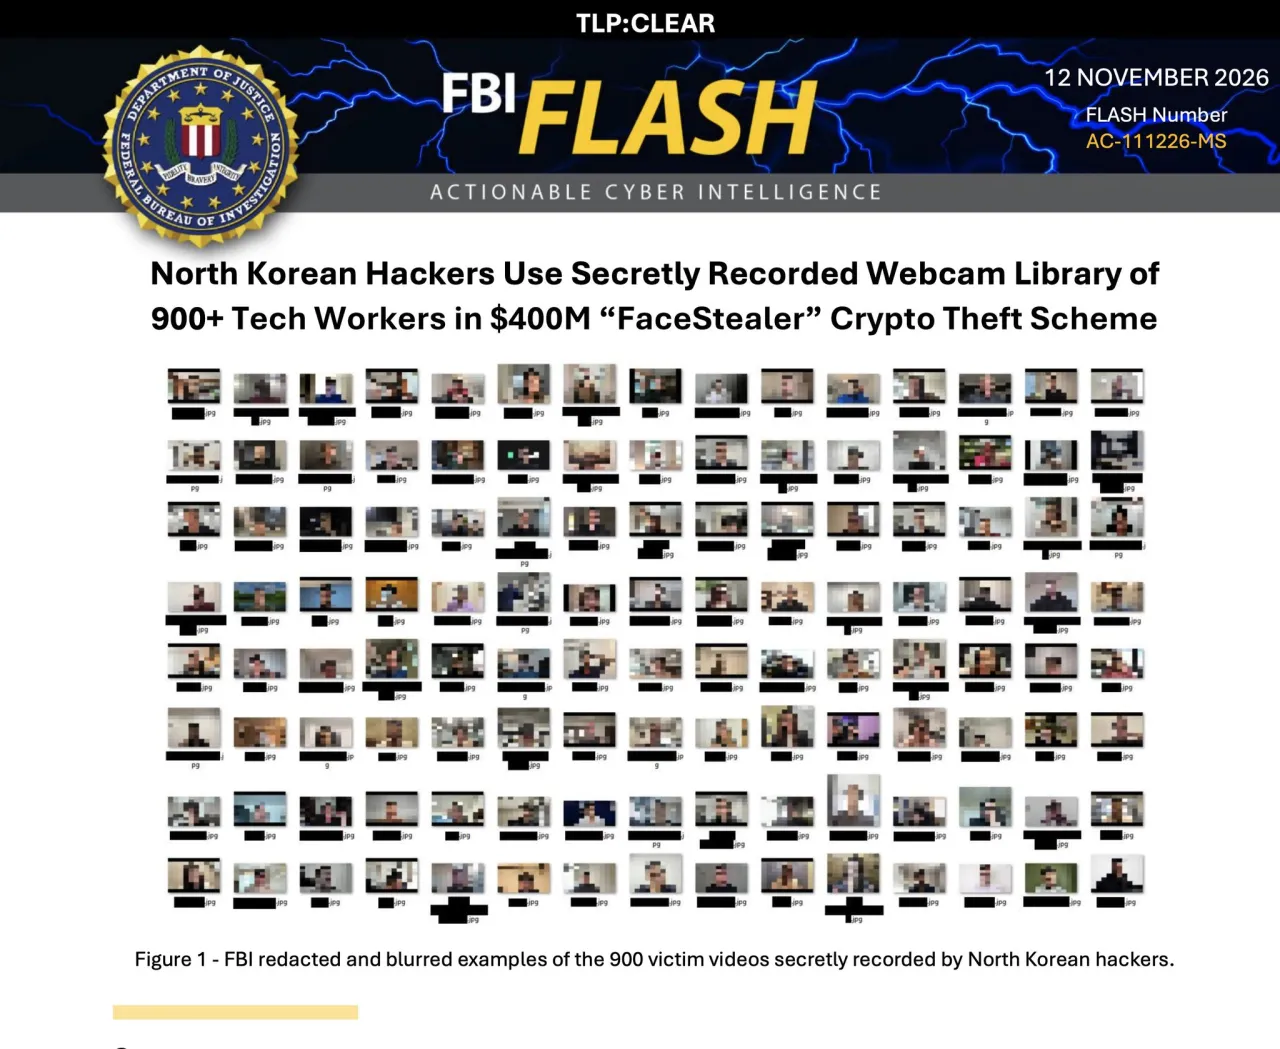
Cybersecurity investigators have uncovered an elaborate hacking operation allegedly linked to North Korean hackers, who reportedly used secretly recorded webcam footage of more than 900 technology workers to deceive victims through fake Zoom and Microsoft Teams meetings.
The operation, identified as FaceStealer, allegedly involved hackers recording unsuspecting individuals through their webcams and replaying the footage during fraudulent video calls to make the meetings appear genuine.
According to the information attributed to the Federal Bureau of Investigation (FBI), the scheme resulted in more than $400 million in cryptocurrency theft over an 18-month period. Authorities have reportedly seized the recorded videos used in the operation.
Investigators say the hackers typically gained access to victims' Telegram or LinkedIn accounts and used the compromised accounts to send seemingly legitimate meeting invitations to their contacts.
During the calls, victims would see familiar faces, making it difficult to suspect that the meetings were fraudulent. The attackers would then simulate audio or connection problems and instruct participants to install software or follow troubleshooting steps.
However, the supposed fix was reportedly a malware delivery mechanism designed to compromise the target's device and gain access to sensitive information.
Once infected, the victim's webcam could also be activated to secretly record footage, which the hackers could subsequently use to impersonate that individual in future attacks.
The operation reportedly extended beyond individual victims, with investigators also uncovering an attempted compromise of a JavaScript software library used by developers and downloaded tens of millions of times weekly.
The attempted supply-chain attack raised further concerns about the potential scale of the operation, as successfully compromising a widely used software package could expose thousands of developers, applications and downstream users.
The reported seizure of the videos represents a significant development in efforts to disrupt the operation. However, the incident highlights the growing sophistication of cybercriminals and the increasing use of artificial intelligence, social engineering and stolen digital identities to bypass conventional security measures.
Cybersecurity experts continue to warn individuals and organisations against blindly trusting video calls, even when they appear to come from familiar colleagues or professional contacts.
Users are advised to independently verify unexpected meeting invitations, avoid installing software through unsolicited troubleshooting instructions, enable multi-factor authentication and promptly secure compromised social media accounts.
The incident serves as another warning that seeing a familiar face on a video call is no longer sufficient proof of someone's identity.
0 Comments
No comments yet. Be the first to share your thoughts.
Leave a Comment