
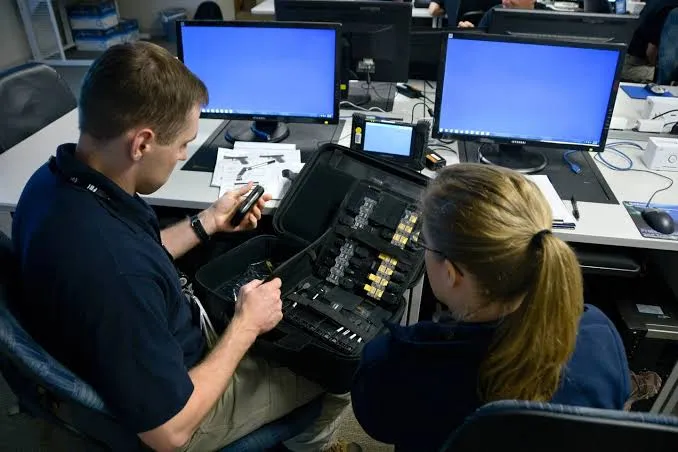
The Federal Bureau of Investigation (FBI) has warned organisations worldwide about the growing use of ARTEX, an artificial intelligence-powered platform allegedly being exploited by cybercriminals to automate multiple stages of cyberattacks.
According to the FBI, ARTEX is an open-source, large language model (LLM)-driven agentic platform that enables threat actors to coordinate and execute different phases of cyber intrusions at machine speed.
The agency disclosed that malicious cyber actors have been using the framework since at least August 2026 in campaigns targeting organisations across several countries and sectors, including financial services, government institutions and technology companies.
The FBI said ARTEX significantly reduces the time required to connect different attack techniques, allowing cybercriminals with limited technical expertise to carry out complex operations against multiple targets simultaneously.
The development has raised concerns about the potential misuse of agentic artificial intelligence tools, particularly their ability to automate tasks that would traditionally require considerable technical knowledge and human involvement.
In response, the FBI has released a FLASH cybersecurity advisory detailing the tactics, techniques and procedures (TTPs), as well as indicators of compromise (IOCs), associated with the ARTEX framework.
The agency urged organisations to study the advisory and implement the recommended mitigation measures to strengthen their cybersecurity defences against ARTEX and similar agentic systems.
The warning highlights growing concerns among cybersecurity authorities about how artificial intelligence tools can be repurposed to accelerate malicious activities and increase the scale of cyber intrusions.
Organisations are encouraged to review the FBI's advisory and take appropriate steps to identify potential threats, detect suspicious activities and protect their networks.

0 Comments
No comments yet. Be the first to share your thoughts.
Leave a Comment